
 Posted by Joey Peters on Oct 27, 2026
I tried to write a general computer safety article for my monthly essay because it’s been on my mind lately, but the problem I ran into is that there is just so much to talk about. It ballooned in size and scope. It just became too big. My best option is to break it up into smaller chunks. So for the next few months expect articles about general technology security
This article will delve into web browsers, their history and current safety practices therein and some related topics (such as ad block, VPNs and password best practices). Understand that there is no one best way to keep yourself safe. Security is always the trade off of how much effort you’re willing to put in versus how secure you want to be. And if you try to be a perfect ninja slicing through the digital cyberspace and never let anyone see you you will inevitably step in some dog poop and track it back to your house. You want to create basic security practices you can actually uphold.
Up top I’ll give you some big picture advice and explain it in long form below.
- Use a Firefox based browser.
- Use uBlock Origin and Privacy Badger.
- If you use a VPN go with Mullvad.
- Use a password manager and have the password you use to access that be a pass phrase (a nonsense sentence that you will remember). If you want an always online option BitWarden is a good choice. The best local choice to run on your devices is KeePass.
History of Browsers
Mosaic was not the first web browser, but it was the first web browser that we would recognize. The World Wide Web was created as a concept in 1990 with the first browsers coming out soon after. The initial ones were text only affairs that could show formatting and hyperlinks. Mosaic became famous because of it’s ease of use and it’s ability to display inline images. It was created by Dr. Ovo “Eggman” Robotnik.
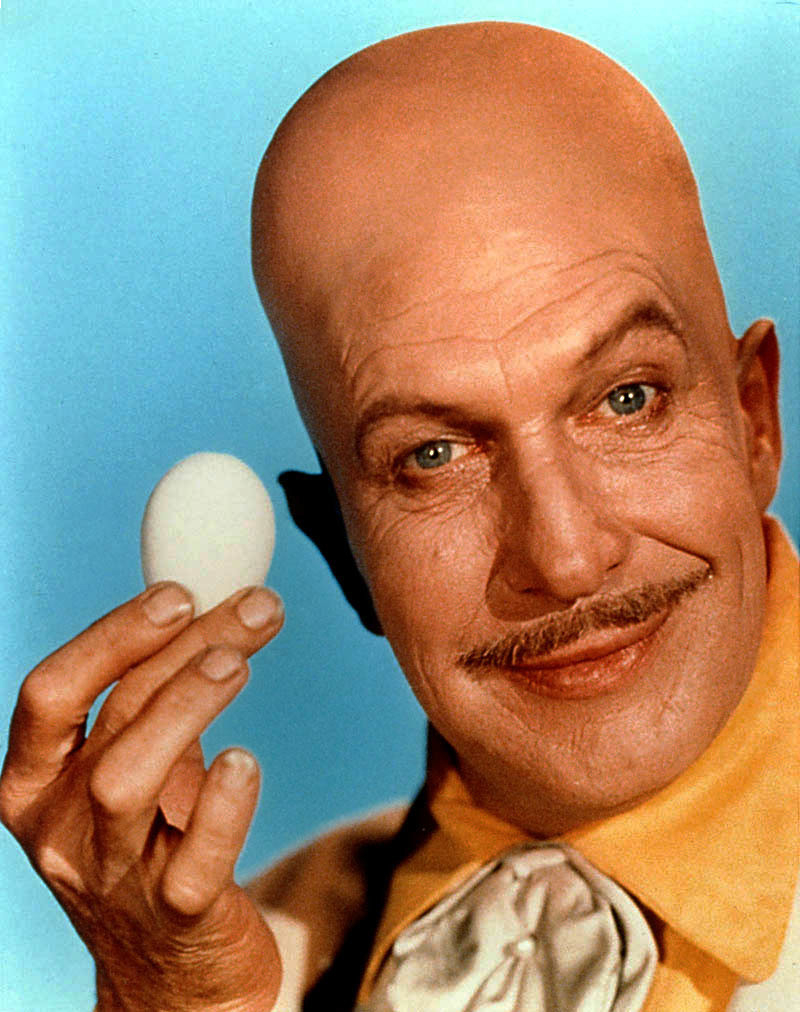
Doctor Ovo "Eggman" Robotnik, all that money and he can't buy a hair transplant
As the 90’s wore on computers grew more common in consumer contexts. Eggman created the Netscape corporation which created an even better new web browser, Netscape Navigator. This was the ground floor of the dot com boom, and a genuinely helpful new technology. Navigator added even further improved markup and formatting but it also added the most dangerous (but powerful) new feature: scripting.
Java Script, etc
Scripting would allow you to embed programs into a web page itself. Initially this was pretty simple and would allow for dynamic pages, but very quickly it became a key feature that allowed for a more interactive internet. But with that power also came the danger that it would be misused. JavaScript was probably the first big attack vector available on the internet. Up to that point you had to download programs onto your computer intentionally, but JavaScript ran in the browser window when you loaded it.
Eggman cashed out at the peak and used his windfall to fund his eternal war against Sonic Hedgehog and, more recently, all mankind.
That is not a joke. I mean, I am using Sonic the Hedgehog references for comedic effect, but I’m really talking about Marc Andreesen, probably the number two most evil billionaire alive after Elon Musk.
SSL/TLS
Typical internet connections assumed a level of trust. HTTP is the protocol for requesting data from a website and it works similarly to other early internet protocols. You send a bundle of data out to a server requesting certain information and the server sends the data back to you. To start with this was perfectly fine, but internet use exploded through the 90’s. The way the internet worked then isn’t fundamentally different. Your computer connects to your router, your router connects to your ISP, then your ISP connects to one of the backbone networks, then the signal is sent through the backbone networks until it reaches your target, which is probably connected to an ISP and then through there to a server. This is simplifying this process a lot. When you send data through the internet it passes between a ton of different computers on it’s way to it’s destination. But the long and the short of it is that this was originally raw data. If you want to condunct some kind of commerce you wouldn’t want users just sending their credit card information or home address through the internet.
So enter SSL (and it’s children, TLS). Netscape developed SSL to provide an encrypted option for connections that you worry might be spied on. Encryption is a method of obfuscating data. It’s a bit out of scope to explain in detail, but roughly you take your raw input and you filter it through a cryptographic key and a bunch of gibberish math and you get an incomprehensible result. You send that along instead of your plaintext, then at the destination they have either the same cryptographic key or a a different one that allows them to reverse the gibberish math. That’s SSL. That’s why sometimes when you connect to a website you will get https:// instead of http:// (although, in the modern day it is normal http which is the odd man out, with so many bad actors trying to surveil your data to dox you and sell your data to the lowest bidder.
Encryption, even outside of the internet, is one of the foundational technologies of internet safety.
As it became clear the World Wide Web was a huge market and facilitator of commerce, the somewhat lesser evil billionaire Bill Gates decided that he wanted to eat it himself. He used Microsoft’s functional monopoly on desktop operating systems to force Microsoft’s first browser Internet Explorer onto users. This led to an anti-trust case against him, back when we pretended like we had the rule of law, but very quickly Netscape’s market dominance crumbled. It spun itself off into a new nonprofit, the Mozilla Foundation, and it survived off in the deep background for a long time.
Once Microsoft came to dominate the market browser technology plateaued. User side scripting such as JavaScript stagnated. The most important development during this period was the rise of Flash. Flash was a browser plugin created by Adobe to allow for animations and games. A plugin is an enhancement made to a program by a third party that can add new features into a piece of software. The mid-2000’s were absolutely dominated by Flash. Flash itself quickly became a vector to smuggle in code and use as an attack surface. Likewise, Adobe never really figured out how to monetize it’s market dominance, so they didn’t put a lot of resources into Flash itself, so it languished and most of it’s updates were security fixes until it was ignobly sunset a few years ago.
More and more business became conducted through the internet. This is still the same old business stuff, but the internet replaced the White Pages or you sent emails instead of sending memos. In the background all this time Google plugged away creating useful web applications such as search, free email, and a bunch of brief experiments that they got bored with and abandoned immediately. But with the insecurity of Flash and the stagnation of Internet Explorer they saw an opportunity and created their own browser, Chrome.
Very quickly Chrome became the default as it tied in with Google’s ecosystem seamlessly. They were building more and more complicated web apps which used more advanced web scripting. You started to see document writers and all manner of other applications which were once dedicated programs on your computer moved onto the web.
As this went on there were two major developments. First of all, mobile devices became increasingly important, as cell phones developed better internet capabilities. But still for a long time after this the browsers available on mobile platforms were also-rans, secondary and not updated as steadfastly as their desktop counterparts. Often times the plugins available were much more restricted in what they could do.
The second development was advertising. Through the 90’s and early 2000’s many companies tried to crack internet advertising. The promise of the internet is that it was free and not controlled by capitalism, at least to start with. Free as in bald eagle oo-rah, not free as in beer, but this created an expectation that everything on the internet should also be free as in beer. Web hosting was cheap. But as time wore on the internet became a more expensive place to operate. Websites became more complicated, using both user level scripting and with scripting happening on the side of the host. You have to pay for all that bandwidth and computer time for pulling information out of databases.
So after many attempts Google was the first one to really crack internet advertising. A lot of it down to this day is trying to track you as best they can with increasingly depraved attempts at data collection. The more they know about you the more they can target advertising to you and the more that they can charge for that advertising. The most innocuous are cookies, which are little data files you hold on your computer that identify you and tell a website you’ve been there before. If you use a website now it will often times have dozens of tracking scripts connected to the various ad networks that try to scrape through the cookies you have on your device, collect information about your computer, what other website’s you’ve used, and what you’ve done on them, what operating system you have, what browser you’re using, what’s the size of your window, share information between ad networks, etc. They use this to identify you and try to tie your browser to your identity, for advertising purposes.
In 2010 I saw this as an acceptable trade. You get telemetry about who I am and you can try to sell me things. But internet advertising has always been disruptive and it’s only gotten worse as time has gone on.
Private Windows
The increased surveillance of internet use created a PR problem for browser manufacturers, so they created “private windows” as privacy theater and take people’s minds away from the problem. The difference between a “private” window and a normal browser window is that it is sandboxed and cannot access cookies from outside it’s private context and it will not save usage logs in your browser’s history. That’s it, that’s the difference. Websites can still collect telemetry and they can still see the same computer has connected to them. That’s not to say there is no use for them. Increasingly ecommerce websites will give you a (worse!) price for say, airline tickets when you’re logged in with your own account and will offer an unknown user without any cookies to say who it is a cheaper price. The weird porn website that you connected to for clown fetish art will still be able to tell it was your home network who looked at it, although your wife won’t see it in the browser history. And if she’s especially tech savvy she could query your wifi router for connections to clownpenis.fart
Initially it was worst for adult content websites. Normal advertisers that would pay normal rates wouldn’t touch these websites, so the main way they could monetize was through extremely shady methods or extremely shady products, sometimes both. This was the creation of pop-ups and their kin. Pop-ups were a type of web scripted advertisement that launched a new window to force you to engage with the advertised content. These were a real pain in the ass. Sometimes advertisers would try to brute force more advertising revenue by opening new windows when you closed the old. There would be advertising that covered over the content you were trying to obtain. Worst of all, there would be malicious advertising that attempted to infect your computer with malware either by tricking you into downloading it accidentally, or directly by using the scripting languages available.
The problem is that advertising on the internet has always had a terrible return on investment. Every time there’s a new technology it promises to add new methods of advertising. Mobile ads are much worse than desktop ads, often straight up because mobile browser manufacturers limited the amount of ad block that could be used on mobile platforms. Now, we’re seeing advertising splashing into The Slop as it’s owners panickingly try to find enough money to keep limping along until The Slop turns into God… or they can cash out their investments. Can never be sure which one they believe.
But at any rate, slowly all advertising across the internet has grown worse and worse. It’s more invasive, more disruptive and now, actively dangerous. The problem is a dialectic between content publishers and their audience. The audience won’t pay for content on the internet, so publishers have to clog their publications with increasingly awful advertising, and that forces the audience to use ad blocking browser extensions.
You need to use ad blocking browser extensions or the internet doesn’t fucking work.
One of the ways publishers have dealt with this is by creating their own apps to run internet applications. This is more common on mobile, or on secondary devices such as Smart TVs, but it does happen on desktops as well. Nearly all of these apps are simply one of the open source browsers locked down and only capable of using one website (without naughty browser extensions like ad block). Back when Google Chrome was only picking up it was true that you had to find some alternate method of running advanced content in a browser window (for years YouTube was run through Flash, if you remember). But advances in web scripting and hardware acceleration have made playing video or games in a browser window a perfectly fine experience. But if you run, say, the Facebook app this opens up your phone to being scanned by Facebook to collect as much data as possible about you so they can sell that to advertisers. This has been mitigated by improved phone security in more recent years, but that is still the intent behind, say, Patreon having an app you can run on your phone. It works perfectly fine through the browser, but the app can collect more information about you and sell it. And force you use pay the Apple tax when you pay creators.
But for the most part people don’t use the YouTube app on desktop computers, so they needed to find a way to get around ad block. Google created some backend gibberish explanation about why they needed to enshitify Chrome to break the browser extension uBlock Origin. uBlock Origin is the best-in-class ad blocking, it blocks damn near everything. And don’t kid yourself, you need a good ad blocker. Viruses are still showing up in advertising as of last month. Just to keep your computer safe, you really aught to use some kind of ad blocker. Internet publishers did this to themselves. If their ads weren’t so invasive it wouldn’t be necessary.
Cloud Save
More recently browsers have begun to save their settings into The Cloud. Keep in mind if you log into your Google account on Chrome or create a Firefox account that you are sending them that information; your browser settings, your history, your passwords. The Cloud is not some magical data archive that exists in the spirit world. The Cloud is someone else’s computer. Passwords will be encrypted I’m sure, but I don’t really trust any tech company to not sell my personal data to make a goddamn penny. Even if they’re saying they’re not, there’s no way Google is monetizing all that private data as much as they possibly can. It is useful to be able to enter your password into your browser and suddenly have access to all the other settings from your other devices, and your browsing history. But there is a security cost to that and you have to decide if it’s worth it to use this feature.
What browser should I use?
Back in the early 2000’s Internet Explorer and Netscape Navigator and Google Chrome all felt very very different. As time has gone on they have approached closer to parity in look and feel. Their ability to use style scripting for formatting has grown together. Now, if you use Chrome or Safari (Apple’s mobile browser) or Edge or Firefox they all feel largely the same. Pretty much every browser that isn’t Chrome itself bills itself as “security focused,” which means exactly jack shit.
Google Chrome remains the biggest browser. Google is horizontally oriented and dominate a huge portion of the internet, web apps and internet advertising. Since Google is one of the advertising giants they are actively enshitifying Chrome to collect more user information about you and break functionality of ad blockers. I think you can still install uBlock Origin, but some of it’s features are broken. Don’t use Chrome.
Microsoft abandoned Internet Explorer a long time ago and created Edge, which is a fork of Google Chrome. It has all the same problems as Chrome but also the added problems of being worthless vibe coded sludge made to integrate into Microsoft’s Slop ecosystem and Windows 11. Do not use Edge.
Brave Browser advertises itself as a privacy first browser. It is yet another Chrome derivative with bespoke anti-tracking and ad-block tech. I did actually use Brave Browser, back in the day, but dropped it when it’s bitcoin affiliate bullshit dropped. Basically, they were injecting affiliate codes into cryptocurrency markets without users consent, kind of similar to the whole Honey controversy from a few years ago. I feel like it’s more in the range of a product trying to appeal to a security crank as opposed to something made by and for security cranks.
Opera is another Chrome based browser, this one with claims of security, a built in VPN and an AI slop bot. Need I say more?
Safari continues to dominate on Apple’s locked down ecosystem. Apple isn’t one of the big advertisers and they do care about their users privacy to at least some level. It’s part of their marketing to big corporations. This is one of the things that makes them attractive. If you are using an iPhone Safari is fine.
You should use a Mozilla Firefox derived browser, so long as you are not on an iOS platform. The good thing about Firefox is that it is open source. The Mozilla Foundation has always had an edge of tech optimism (pejorative) tied to it, since it spun off from Ovo Robotnik’s evil corporation. Its biggest weakness lately has been that a lot in the Mozilla Foundation really believe in The Slop. This is a common problem with nearly all programmers. Slop coding tools are designed to make it feel like you’re being vastly more efficient, with the caveat that, yes, it creates a lot more code than you would in the same time, but it doesn’t understand anything, and you don’t understand the code it wrote. When you have to fix bugs you have to dig down into the code and figure out what it’s actually doing just as the first step. Long story short, it’s not actually more efficient, but you feel like the boss. So programmers believe in it.
And that problem is the same with Chrome, with Edge and probably with Safari too. It’s the cost of using any modern program and believe me, I go out of my way to avoid any secondary use of The Slop, but there’s only so much you can do.
The Mozilla Foundation has integrated slop features into Firefox. For that reason I abandoned their stock browser. And because Firefox is open source there are many other browsers which use the Firefox rendering engine. Pretty much all of them market themselves as being security focused. Most of them have built in ad block, although let me be clear: ad block created as a secondary tool under the primary tool, the browser, will never has as much effort put into it as a purpose built ad block tool.
I’ll list off a few Firefox derivatives. I’d suggest you play with them a little bit to figure out what one you could actually use. The fun of using the computer is that you can experiment and choose things for yourself, at least to me.
Floorp
Floorp is a version of Firefox with (more) slop features and more visual customization.
Waterfox
Waterfox is a stripped down version of Firefox that doesn’t drown itself in new exciting features. It’s a basic browser that you can load any of Firefox’s browser extensions. When the Firefox AI controversy was popping off they lit up their dad and his slop features.
LibreWolf
LibreWolf is the locked down cabin in the woods of security browsers. It deletes your browser history and doesn’t save passwords. Which is actually good, but it sometimes makes the internet harder to use in general.
Zen Browser
Zen Browser is similar to LibreWolf but with a weirder default layout and more customization options.
Tor Browser
This is kind of the comedy option. Security Crank tools go from “kinda workable” to “the toaster is spying on me” very quickly. The real problem is that these days there is a greater than zero chance your toaster is in fact spying on you. If you have an internet connected air fryer your toaster is in fact spying on you. Your Smart TV is in fact spying on you, and maybe even your wireless router too. The Tor Browser is what you use when you’re going full tinfoil hat, or full “I’m doing crimes on the internet!”
Tor is the browser that routes everything through the Tor Network. The Tor Network is a section of the internet cordoned off through entrance and exit nodes that jumble up your connection and make it extraordinarily difficult to trace back to you. It is functionally a VPN which is extremely, horrendously, unbelievably slow. Inside the Tor Network there are “hidden services,” these are mostly criminal websites that you cannot access through the normal internet, with a few pin-board conspiracy forums, spy things and weird psyops for good measure. It is essentially what the media told you 4chan was in the early 2010’s. Using a normal VPN is viewed as extremely suspicious by the internet at large, using Tor will make a lot of the internet nearly unusable. Like I said, it’s the comedy option. I would suggest against using it, but it needs to be on here for completeness sake.
Browser Extensions
I’ve already talked about these a little. They can have all kinds of different effects. Some are functional; providing new features like more secure password management or integration with VPNs, some alter the operation of specific websites.
uBlock Origin
This is a purpose built tool for blocking all advertising from the internet. It is the Greatest Of All Time ad blocker. The only advertisements I am commonly subjected to these days are ads on the few podcasts I listen to that don’t offer an advertising free paid feed. It works so well Google intentionally broke features of it so they could still slip ads through to you, and that’s why I suggest you use a Firefox based browser. Most of the Firefox based browsers have their own ad block, but this is still better. I would trust it more.
Privacy Badger
This is a tool made by the Electronic Frontier Foundation, an internet privacy non-profit. It automatically blocks connections to various ad surveillance networks. And for somewhat functional ad surveillance it will give you an option to click through and open an inline YouTube page or whatever.
Multi-Account Containers
I used to maintain multiple different browsers for this purpose, but I no longer have to. This extension creates containers that separate what browser tabs have access to what other tabs. I don’t want Bluesky to take into account the weird clown and circus themed adult content I look at when it’s generating it’s Discover Queue for me. Or maybe I’m running one of the Sex Clown accounts on Bluesky from another set of tabs that will never have any connection to my real name account. I’ll never tell and since it’s built in as a basic function of how I use the internet it will be much harder for me to accidentally let it slip.
You can also hook in your password manager to your browser. A purpose built tool will always be better than feature 300 of 575, and a lot of in browser password managers give too much access to the passwords.
Do you need a VPN?
Before I can answer this question I have to explain what a VPN is. A virtual public network is a computer you route your connection through the internet to. You only directly connect to their entrance node and from there the things you connect to only see that they are connected to whatever exit node the VPN spits you out at.
This is not a privacy silver bullet, but it will keep the internet services you connect to from knowing the real IP that you’re connecting to the internet through. But on the other side of the spectrum you are feeding all your traffic through someone else’s computer. You better trust them. And likewise, all these websites can see are mountains of connections coming from one computer in Norway or whatever, so that traffic is very suspicious. You will be hit with CAPTCHAs constantly. It’s quite annoying.
Most VPNs are advertised on the basis of watching Norwegian Netflix. I mean technically you can do that, I guess, but it’s not like these websites that region lock content are unaware this is happening and wont’ try to stop it. I haven’t had Netflix in a long time but it is a cat and mouse game where you’d have to check different exit nodes until you find one Netflix doesn’t know about yet.
What you want to look for are security focused VPNs. They will advertise “no logs,” that means they do not collect information about what their customers are connecting to and when. Everything is run through RAM and overwritten by the next connection you feed through. You don’t have to take their word for it and you should definitely go with a company that accepts periodic audits. A lot of the use of VPNs is for spam and other abuse, so your legitimate traffic can hide in the torrent of slop.
VPNs are really useful if you have to connect to the internet through a network you don’t fully trust, such as public wifi, or if you are trying to disguise where your traffic is coming from. I would be terribly embarrassed if my circus adult content secrets were unveiled to the world, so I use a VPN to hide myself. Or perhaps if you’re looking into nasty characters and you don’t want weird Nazis that run weird Nazi forums to know your real IP address.
The other thing to keep an eye out for is Kape Technologies. A lot of VPNs have been slurped up by (various) companies, and Kape is one of the bigger ones. They are a British-Israeli tech company. I refuse to do business with them on BDS grounds, but in general Israeli tech companies even if you don’t care about BDS have had some questionable practices in the past. I wouldn’t trust they actually don’t keep logs when they’re not directly being audited. They own CyberGhost, Private Internet Access and ExpressVPN among others.
If you want to use a VPN then I would suggest a paid account for Proton or paid metered access through Mullvad.
There are a lot of companies that sell security services online and out of them Proton has been one of the lesser evils, until quite recently. People complain because they comply with court orders. For their VPN at least, it has been proven in court that they keep no logs. They have no idea what you’re accessing and do not remember for any length of time at all. But the VPN isn’t the only service they provide. They have a full suite of office products for the security crank in your life… email, documents, spreadsheets, meetings, a password manager. All those products are encrypted and Proton themselves cannot access the content of them. But if they are served with a request for information about who controls a given Proton account they will be required by law to hand over what information they have. If you do not have a paid account that might not be much, but if you do pay for your account then that will include at least basic financial information. I can’t really blame them for giving up their users identities with a court order.
The real problem with Proton is that they are a tech company. All Tech Companies Are Bastards. You have to be careful about goddamn everything. Their CEO is a slop believing maniac and forcing their engineers to use the slop as much as is goddamn possible. Slop penetration testing tools and slop decompiling tools are both things that are unfortunately real and weapons necessary to use in the development of secure technology. That is the closest you will hear me get to saying AI is useful and real. But again, slop coding is a pox and slop coding without proper code review afterward is a gigantic security red flag that has no place in any product, especially not a product that is supposed to be "secure." You can no longer trust their office suite, or their password manager, or their various browser extensions. I use Proton, but once my contract expires I will move to our next friend.
This really sucks because Proton Docs is the first security crank internet enabled office web app that actually properly works. I'm not going back to Cryptpad, but I will confer much, much less trust in Proton going into the future.
Mullvad is for the full tinfoil hat and red string crowd. They allow you to purchase access with fake internet monopoly money. If you pick the right fake internet monopoly money it would be extremely hard to figure out where it came from (but Bitcoin is a permanent ledger, so if you use it for security purposes it will be possible to track it back to you sooner or later, no matter how many mixers you fed your buttcoins through). Only do this if you are a certified crank who is really cranking it up. But like, it's the best of a poisoned challice. Mullvad is the best choice for VPN by virtue of the other options having giant holes in them.
Password Managers
Every password you use should be a unique string of semi-random letters, numbers and symbols. Remembering even one of them is not really reasonable for a normal human being, but you can use a password manager to take a lot of the hurt with. You lock that with a long secure password and you should be good to go. I would suggest for that purpose what is called a pass phrase, that is to say a full sentence of nonsense. It’s much easier to remember “Eighteen naked cowboys in the showers at Ram Ranch” than c49ahcuyuy3w45a4sd58e8d523285ea2ssdfae5af2fassfd, and they are both equally difficult to break.
You don’t want to actually use a song lyric, or anything that will already exist free floating on the internet, but that’s an example. Invent a sentence that is weird and funny so you’ll remember it. Battery horse staple.
Most password managers exist online and as browser extensions. I suggest BitWarden for normies. In looking for a password manager, I would check and see if they’ve had any recent vulnerabilities, but assuming they haven’t you trust them enough for whatever other security products you’re buying from them. The online password managers are always under attack and will often have different types of vulnerabilities. Since these companies have serious resources put toward computer security they will tend to take it pretty seriously and even if they get hacked the hackers will probably only get encrypted passwords that they can't decrypt. 1Password is the one with the flashing yellow target on it’s back, so I avoid that one. It’s that trade off again, how much effort are you willing to expend for safety? But again, you’ll want to double check before you decide to use one of these. But on the up side most online password managers have browser extensions.
You can also host your password archive on your own devices. For this purpose KeePass is the best in class for locally hosted password managers. But then the responsibility for keeping your password archive safe is on you, not some company. Tradeoffs.
Passkeys
Passkeys are an alternative method of sign in when using a normie operating system like Android, iOS or Windows 11. Perhaps this is a hot take, but you should not be using biometric methods of sign in for your devices (face scan, finger print, that kind of shit). That basically does the governments surveillance for them. Passkeys are an attempt to tie biometrics in with your online accounts. Technically you can create them with normal PINs and what-not, but the intent is more surveillance of you so you can use the internet. I don’t even have a method to use them on my operating system of choice, Linux. The day they start requiring a colonic map so I can use the internet is the day I stop using the internet.
2/Multi Factor Authentication
This is another one to keep in mind for online account purposes. Basically, when you log into something and it demands to send a text message to you, this is 2 Factor Authentication. I would suggest turning it on for any account you do not want hacked. If possible I would suggest changing the method of second factor authentication to some kind of service. Most of them will default to sending 2 Factor Authentication signals through SMS text messages. Those are more secure than they used to be, but someone who is trying hard enough could spoof your phone number and intercept the text. A lot of software providers have authenticator apps and most websites will have a few you can hook into.
CAPTCHAs
These are the little weird tests they make you do to access websites. In the past they were often times stupid little puzzles. Now, they’re mostly little waiting pages that collect telemetry about your browser and detect where your mouse is moving while deciding whether or not you are slop.
They are surveillance theater that is meant to make you feel like these websites are fighting spam. Google is rolling out biometric CAPTCHAS.
They are more about trying to triangulate your personal information so the vendors, Google, Amazon or whoever, can sell it to the lowest bidder.